Penetration testing. Red team. Vulnerability research.
Penetration testing for Australian organisations across applications, infrastructure and connected devices, with findings your team can verify and fix.
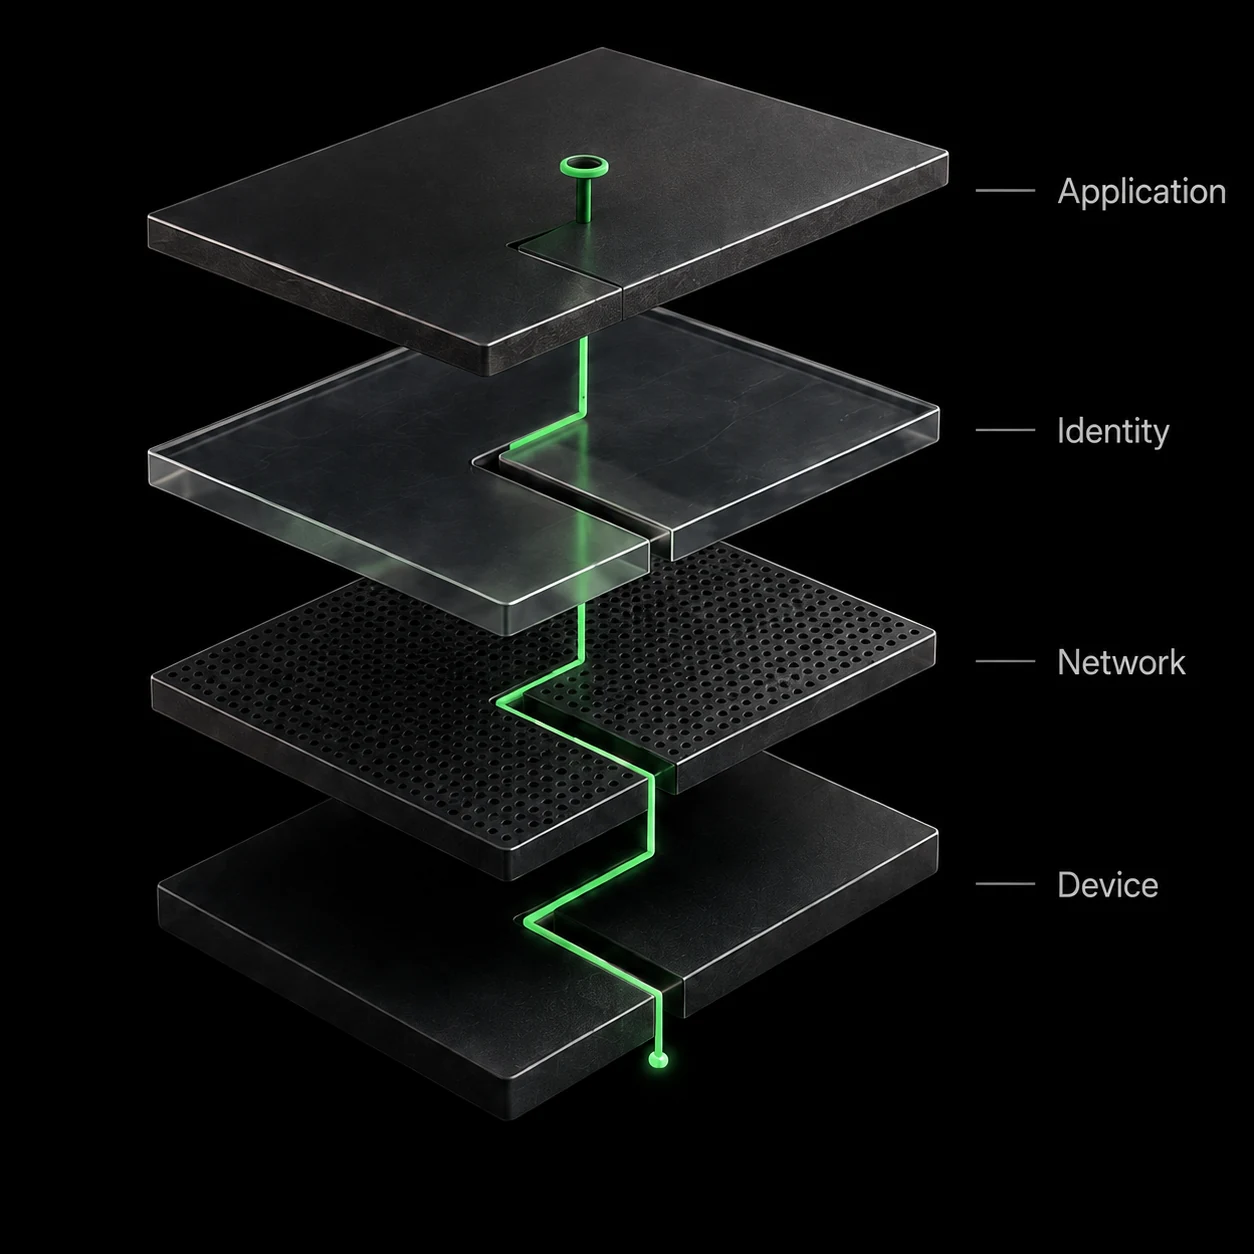
Our security testing services
Published research
The Debrief
Vulnerability analysis, testing notes and practical remediation.
Read the latest issuePublished work
Read the work behind the services.
-
12 Aug 2026
Whitepaper
Human-led offensive security in the age of AI
Practical governance for using AI across offensive security without weakening human judgement, operational control or evidence quality.
→ -
11 Aug 2026
Debrief 003
U-Boot parser, TP-Link MR600 V5, and router hygiene
Independent U-Boot reproduction, MR600 V5 fix analysis, and source-backed OT and IoT signals.
→ -
5 Aug 2026
Vulnerability research
Pre-auth stored XSS in Formidable Forms
How an unauthenticated SVG upload became same-origin JavaScript in a logged-in WordPress administrator's browser.
→
Professional standards
CREST Pathway organisation.
Neonix Security is listed on CREST's Accreditation Pathway.
Our Pathway status and verificationWork directly with the people doing the testing.
Our consultants scope the engagement, carry out the testing, and work through the findings with your engineers and security team.
About NeonixEmail is the fastest way to reach us
hello@
We typically reply within one Australian business day.
- Location
- Melbourne · Brisbane · Sydney
- Hours
- Mon – Fri
- Response
- Typically within 1 Australian business day